Home
About Us
Why Digitalis
Solutions
By business capability
Real-time streaming
Always-on platforms
Time-series data
Enterprise SaaS
Data for AI
By industry
Financial services
IoT & connected devices
Energy & utilities
Telecoms & media
Technology & SaaS
All solutions →
Services
Data Engineering Solutions
AI Services
Consulting Services
DevOps Services
Migration & Modernisation
Move to Open Source
Managed Services
Managed SIEM
All services →
Technologies
Apache Cassandra
Apache Kafka
PostgreSQL
Elasticsearch
ClickHouse
Kubernetes
Scaleway
Cloud Agnostic
All technologies →
insights
Case Studies
Blog
Contact
Let’s Talk
< ALL BLOG POSTS
Category:
Security
View all
Category one
Category two
Category three
Category four
Category
Secure access to AWS with OpenBao
Replace long-lived AWS access keys with short-lived STS credentials from OpenBao that expire on their own, and keep the root key out of reach.
Read more
Category
Dynamic credentials with OpenBao and Vault
Swap static database passwords for dynamic credentials: users created on request and dropped when the lease ends. How we run it on OpenBao and Vault.
Read more
Category
Migrating from HashiCorp Vault Enterprise to OpenBao or free Vault
Most teams leaving Vault Enterprise only use features OpenBao and free Vault already have. The hard part is configuration, so we built a tool to migrate it.
Read more
Category
Immutable virtual machine images, part deux
Turn one hardened golden image into a fully configured, environment-specific node on first boot with cloud-init, systemd and vals, with no configuration drift.
Read more
Category
Hardening the Software Supply Chain
A practical guide to hardening your software supply chain using Cosign, Kyverno, Harbor, SHA digests, and SBOMs.
Read more
Category
A practical guide to post quantum encryption
A practical engineering guide to future-proofing server access by enabling ML-KEM hybrid post-quantum key exchange in OpenSSH 9.9 and 10.0.
Read more
Category
AI Assisted Programming
How We Mastered AI-Assisted Development: Planning, Agents, and the Power of CLAUDE.md
Read more
Category
Kubernetes and Wireguard: CNI vs VM
Kubernetes CNI-native WireGuard encryption versus a VM-level WireGuard underlay: the technical differences, pros and cons, and how to choose for your cluster.
Read more
Category
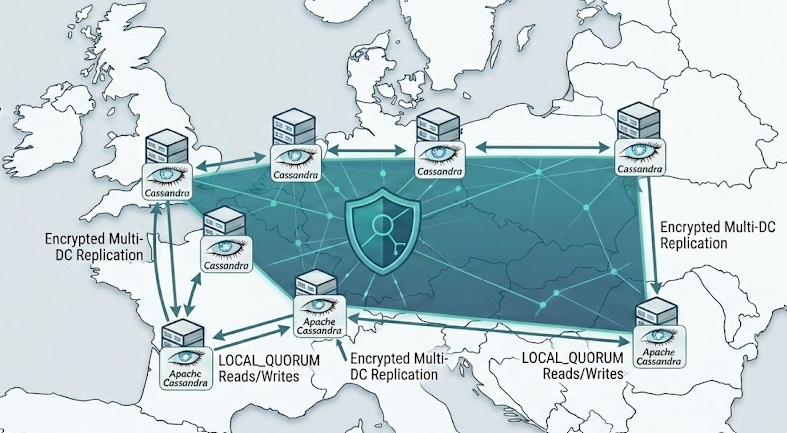
Meshing with Cassandra - Cloud-Agnostic Resilience Blueprint
A blueprint for multi-DC Apache Cassandra across sovereign European infrastructure, using a WireGuard mesh for data autonomy and vendor-neutral security.
Read more
Category
Immutable servers: security and repeatability all in one
Build immutable server images with Packer and Ansible instead of patching live boxes over SSH, for more secure, repeatable infrastructure.
Read more
Category
Plugging the Gaps: Achieving Cloud Sovereignty Through OpenBao’s Modular Architecture
In an era where proprietary licensing can threaten operational stability, OpenBao emerges as a vendor-neutral alternative for secrets management.
Read more
Category
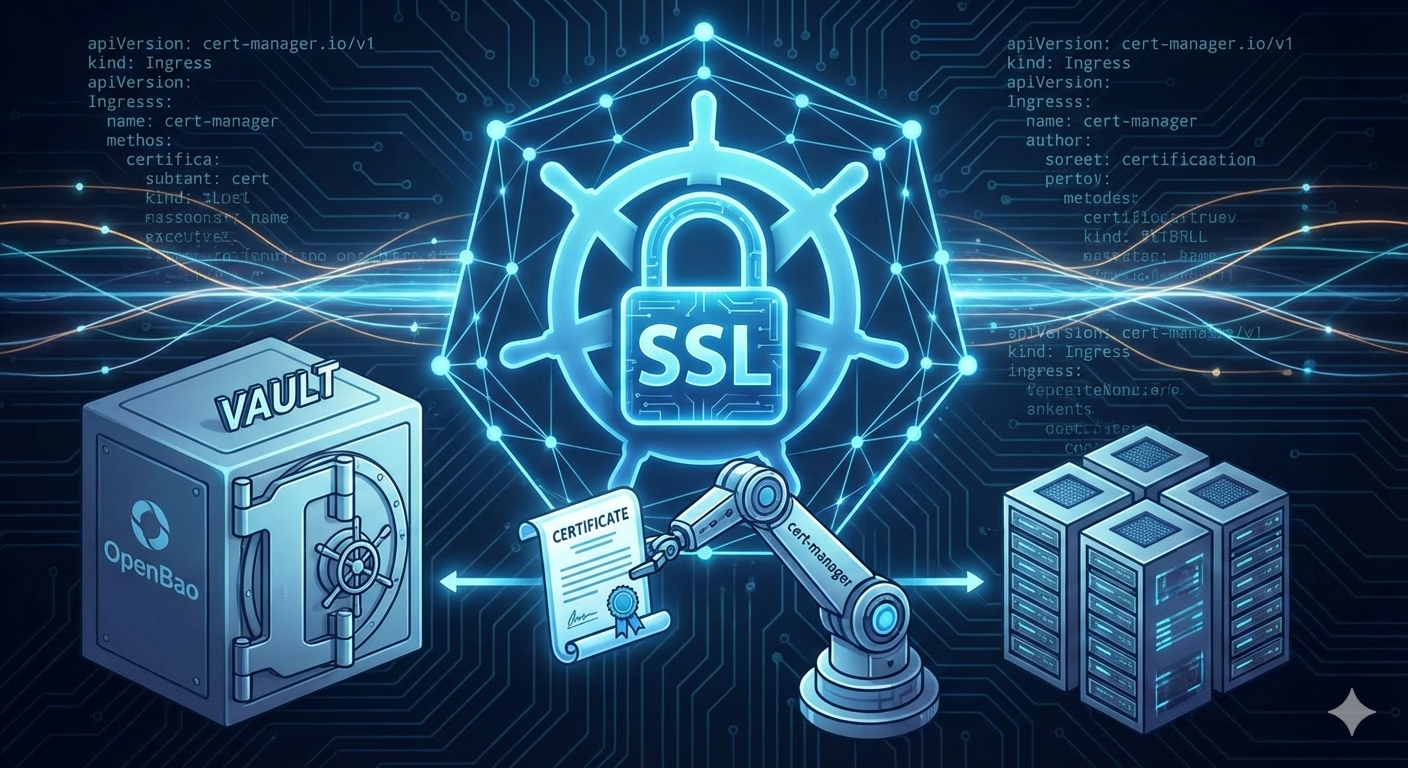
Encryption by default: Managing SSL generation in Kubernetes
Stop managing certificates manually. Learn how to automate Kubernetes SSL/TLS for Ingress and internal services using cert-manager, Vault, and OpenBao.
Read more
Category
Choosing a secrets storage: HashiCorp Vault vs OpenBao
Discover how OpenBao, the open-source alternative to HashiCorp Vault, delivers secure, community-driven secrets management.
Read more
Category
How to Reset a Lost Cassandra Superuser Password
You can't recover a lost Cassandra superuser password, but you can reset it. Why versions differ on authentication and a step-by-step recovery guide.
Read more
Category
Why Enterprise Data Platforms Are Still Insecure
Enterprise databases keep getting breached through weak encryption, poor access control and misplaced trust in internal systems. Why, and how to fix it.
Read more
Category
Collecting metrics, traces and logs
Our simpler standard for collecting metrics, traces and logs: why we moved away from the legacy model and what a lean observability setup looks like.
Read more
Category
The risks of AI to your data
Pasting company data into public AI tools carries real risk. What can go wrong with AI and LLMs, and how to protect your organisation's data.
Read more
Category
Why and how we collect logs
Why log collection is more than a compliance checkbox, and how we collect logs to gain insight into security, performance and reliability.
Read more
Category
Back to foundations: SSH
Back to basics with SSH: using SSH agent for key management, proxying connections through jump hosts, and security best practices.
Read more
Category
Tricks of the trade: working with environments
How a managed services team switches safely between many customer workloads and environments without running commands against the wrong one.
Read more
Category
Strimzi Kafka with Traefik Ingress and custom CA
Secure external access to a Strimzi Kafka cluster on Kubernetes using Traefik ingress and your own certificate authority instead of self-signed certificates.
Read more
Category
Traefik Ingres with Mutual TLS in Kubernetes
How we secure Kubernetes ingresses with mutual TLS using Traefik TLSOptions, cert-manager and HashiCorp Vault, plus the gotchas we hit.
Read more
Category
Rotating database credentials
How we remove static database passwords with HashiCorp Vault dynamic credentials and the vals-operator DbSecret, so access expires within an hour.
Read more
Category
Cassandra SSL certificates rotation
Rotate Apache Cassandra SSL certificates often using HashiCorp Vault as the CA and consul-template, reloading SSL without restarting nodes.
Read more
Category
Vals-Operator 0.6.2
Vals-Operator 0.6.2 syncs secrets from external stores into Kubernetes secrets. This release updates core libraries and adds secret templates.
Read more
Category
Kubernetes Network Policies with Calico
We’re going to look at how to manage network policies in Kubernetes with Calico.
Read more
Category
Kubernetes Network Policies
An introduction to Kubernetes Network Policies: how to isolate workloads and control pod-to-pod traffic, with practical examples you can apply.
Read more
Category
Vals-Operator: Managing Kubernetes Secrets
Introducing vals-operator — an opensource tool for managing secrets in Kubernetes
Read more
Category
Securing Access to Kubernetes with Rancher
The built-in ones are good for most use cases. They are pretty granular covering access to Rancher itself down to individual projects or…
Read more
Category
Kafka Installation and Security with Ansible - Topics, SASL and ACLs
This blog shows you how and provides a fully working Ansible project on Github to install Kafka and manage its security.
Read more
Category
Apache Kafka and Regulatory Compliance
How Kafka can help meet regulatory standards and compliance when used as an event broker to Security Information and Event Management (SIEM) systems.
Read more
Category
Prometheus Blackbox-Exporter - monitoring TLS certificates
A short blog on how to monitor SSL certificate expiry on databases such as Apache Cassandra using Prometheus and visualise on a Grafana dashboard.
Read more
Category
Kafka Connect gotcha - SSL
Unexpected out-of-memory errors in Kafka Connect over SSL? Configure SSL separately for internal connections, consumers and producers.
Read more
Category
Simple tips for securing Cassandra
This blog outlines some good practices that can help you secure your Apache Cassandra clusters.
Read more
Ready to Transform
Your Business?
Let’s Talk